Enterprise operations
Security, privacy and assurance
Understand implemented boundaries and the evidence still required for independent assurance.
In this document
Authority is enforced on the server#
Tenant membership, application key scope, current assignments and explicit administrator authority determine access. Navigation visibility is not the authorization boundary. Revoked or expired credentials and stale dependent authority must not retain permission because a client still displays an earlier state.
Provider and connector integrations require explicit destination and secret controls. A private deployment must preserve those checks in its actual network, identity and operations configuration.
Do not assume every record has the same privacy model#
Ordinary decision telemetry primarily records derived findings, versions and digests. Uploaded assessment material, connector diagnostics and encrypted exact-output review artifacts follow distinct storage paths. Review their access, purpose, retention and support-sharing requirements separately.
Hashes are not anonymization. A public synthetic evidence packet is not a template for publishing arbitrary customer requests. Public demonstration telemetry and private tenant evidence have separate publication and authorization boundaries.
Operational evidence matters#
Security qualification includes configuration review, recovery exercises, dependency and patch management, incident procedures, isolation testing and independent assessment appropriate to the intended use. A passed local regression suite establishes particular software behavior under its test conditions; it does not certify an entire deployed service.
Use approved channels and scoped diagnostics for security or support review. Avoid including raw keys, credentials or unnecessary customer content in tickets, exports and screenshots.
SOC 2 readiness is an early discussion#
LSAS is in early SOC 2 readiness discussions with Vanta. This is a planning fact supplied by the owner, not a completed audit or independent attestation. Readiness tooling and an auditor's opinion are different things.
LSAS does not currently claim SOC 2 Type I or Type II attestation, ISO certification, clinical validation or equivalent independent assurance. Any future claim must identify the actual report, scope and period rather than infer certification from software features or a vendor relationship.
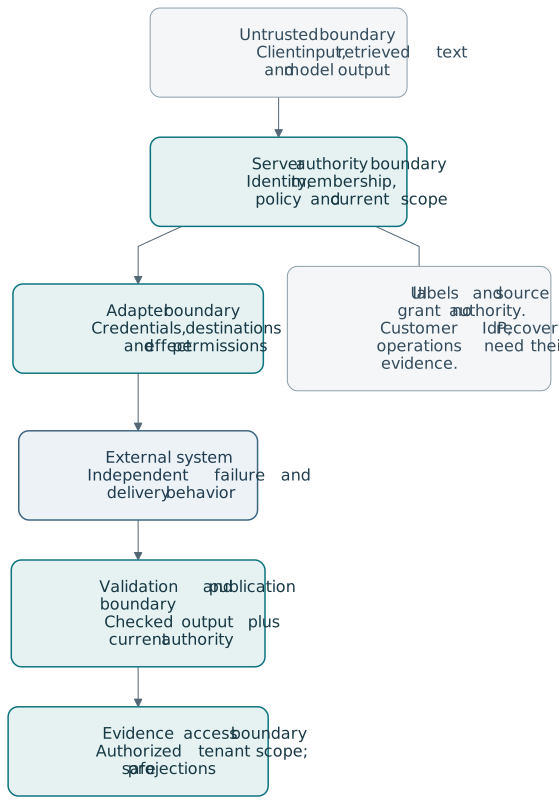
Untrusted clients and content cannot grant authority. Server authorization, qualified adapters and scoped evidence each have separate responsibilities.
Architecture boundaries; no certification or complete customer-environment qualification claim.
Read the diagram description
Untrusted clients and content cannot grant authority. Server authorization, qualified adapters and scoped evidence each have separate responsibilities. Architecture boundaries; no certification or complete customer-environment qualification claim.