Architecture library
Relationships, made explicit.
Shared visual conventions across the governance operating model. Read the scope beside each diagram: a proposed relationship is not an implemented control.
Browse diagrams
- d01 · The governance operating model
- d02 · Alignment: proposal to authority
- d03 · Scope and accountable ownership
- d04 · Three adoption contexts
- d05 · Two governance dimensions
- d06 · Policy versions and runtime binding
- d07 · A supported runtime request
- d08 · Where the Gateway governs
- d09 · Enterprise AI egress
- d10 · Shadow AI Intelligence
- d11 · Tokenomics and cost attribution
- d12 · From execution to retained evidence
- d13 · Regulatory Pulse: sources before conclusions
- d14 · Provider-independent governance boundaries
- d15 · Deployment patterns and qualification
- d16 · Qualifying enterprise scale
- d17 · Scoped reporting and accountable interpretation
- d18 · Permission, content and final release
- d19 · Two parallel evaluation paths
- d20 · Trust is established at each boundary
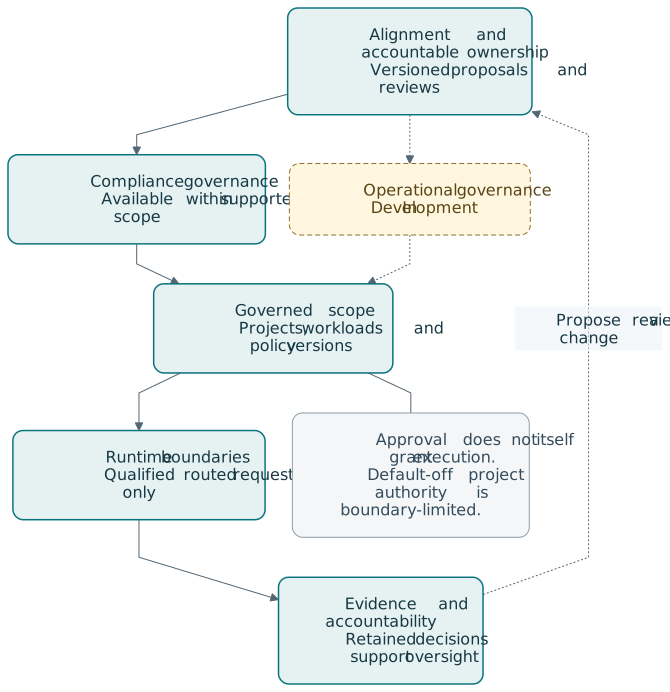
Organizational alignment and accountable scope connect to supported runtime controls and retained evidence. Operational extensions remain in development.
Conceptual relationship; organizational approval is not executable enforcement.
Read the diagram description
Organizational alignment and accountable scope connect to supported runtime controls and retained evidence. Operational extensions remain in development. Conceptual relationship; organizational approval is not executable enforcement.
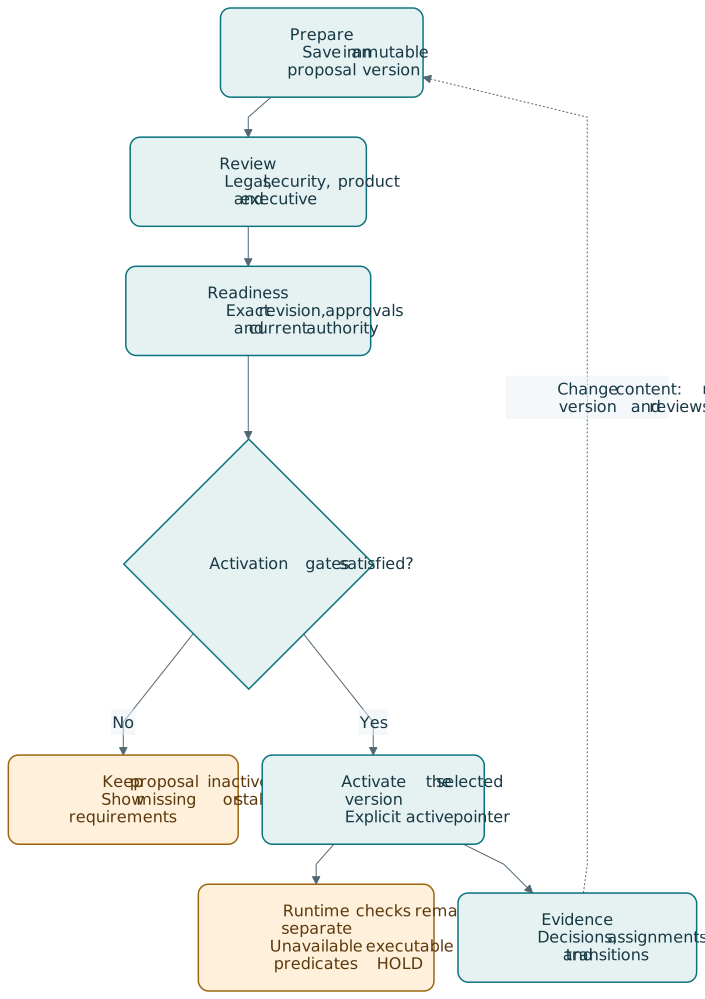
Prepare an immutable proposal, obtain independently assigned reviews, assess the exact version, and activate only through existing gates.
Current workflow; activation and runtime enforcement are separate checks.
Read the diagram description
Prepare an immutable proposal, obtain independently assigned reviews, assess the exact version, and activate only through existing gates. Current workflow; activation and runtime enforcement are separate checks.
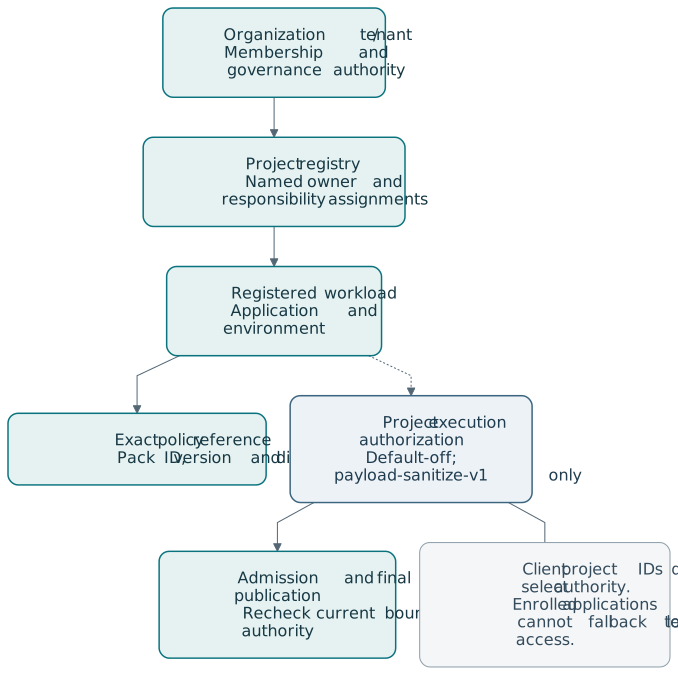
Organization, project, workload and exact policy references constrain interpretation; inventory alone never grants permission.
Registry is implemented; project execution authority is default-off and limited to payload-sanitize-v1.
Read the diagram description
Organization, project, workload and exact policy references constrain interpretation; inventory alone never grants permission. Registry is implemented; project execution authority is default-off and limited to payload-sanitize-v1.
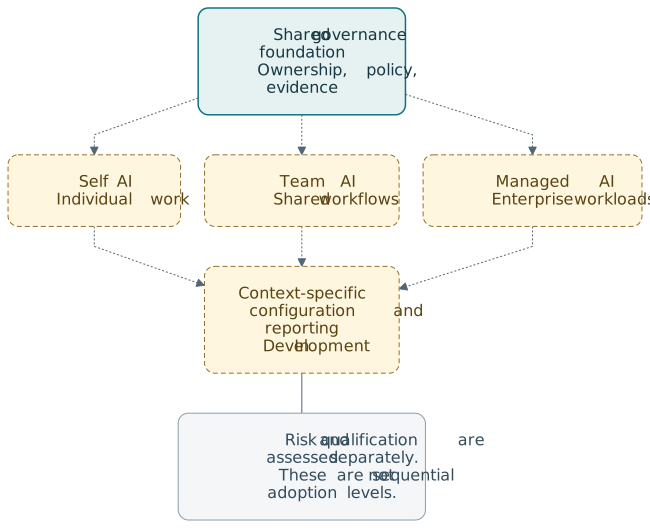
Self AI, Team AI and Managed AI describe operating contexts, not maturity steps, risk ratings or subscription tiers.
Profile configuration and contextual reporting are In Development.
Read the diagram description
Self AI, Team AI and Managed AI describe operating contexts, not maturity steps, risk ratings or subscription tiers. Profile configuration and contextual reporting are In Development.
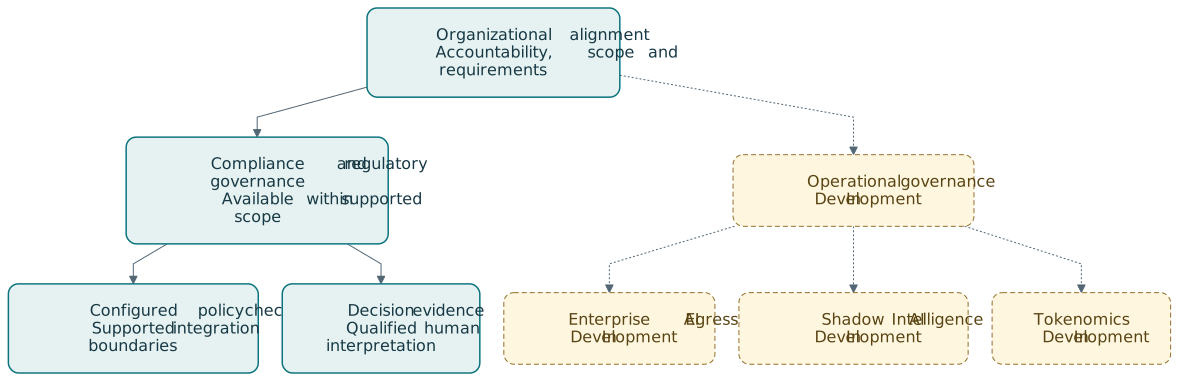
Compliance and regulatory governance uses scoped policies and evidence. Operational governance describes planned network, discovery and cost capabilities.
U.S.-first supported policy scope; no legal compliance certification.
Read the diagram description
Compliance and regulatory governance uses scoped policies and evidence. Operational governance describes planned network, discovery and cost capabilities. U.S.-first supported policy scope; no legal compliance certification.
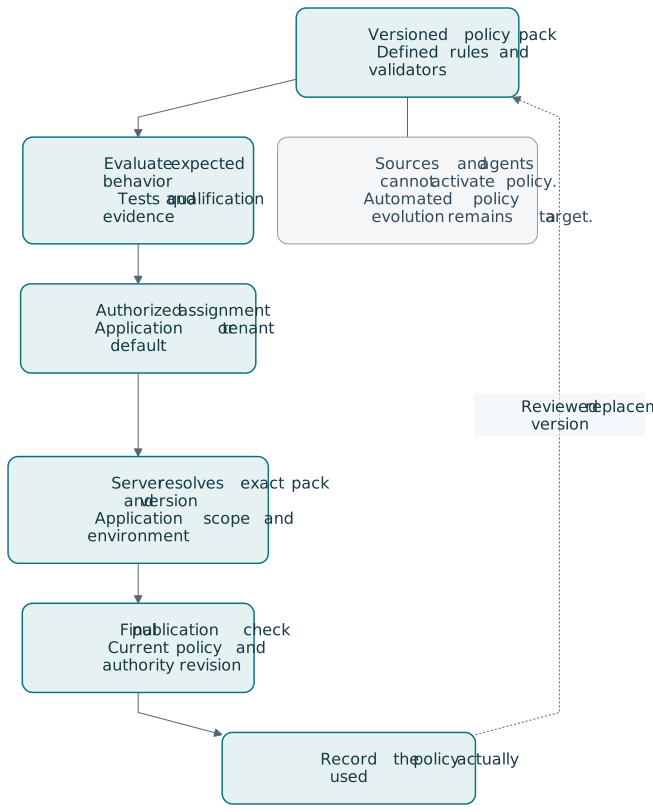
A versioned policy is evaluated and explicitly assigned; the server resolves the exact applicable binding and rechecks it before release.
Current version binding; autonomous source-to-policy promotion is not implemented.
Read the diagram description
A versioned policy is evaluated and explicitly assigned; the server resolves the exact applicable binding and rechecks it before release. Current version binding; autonomous source-to-policy promotion is not implemented.
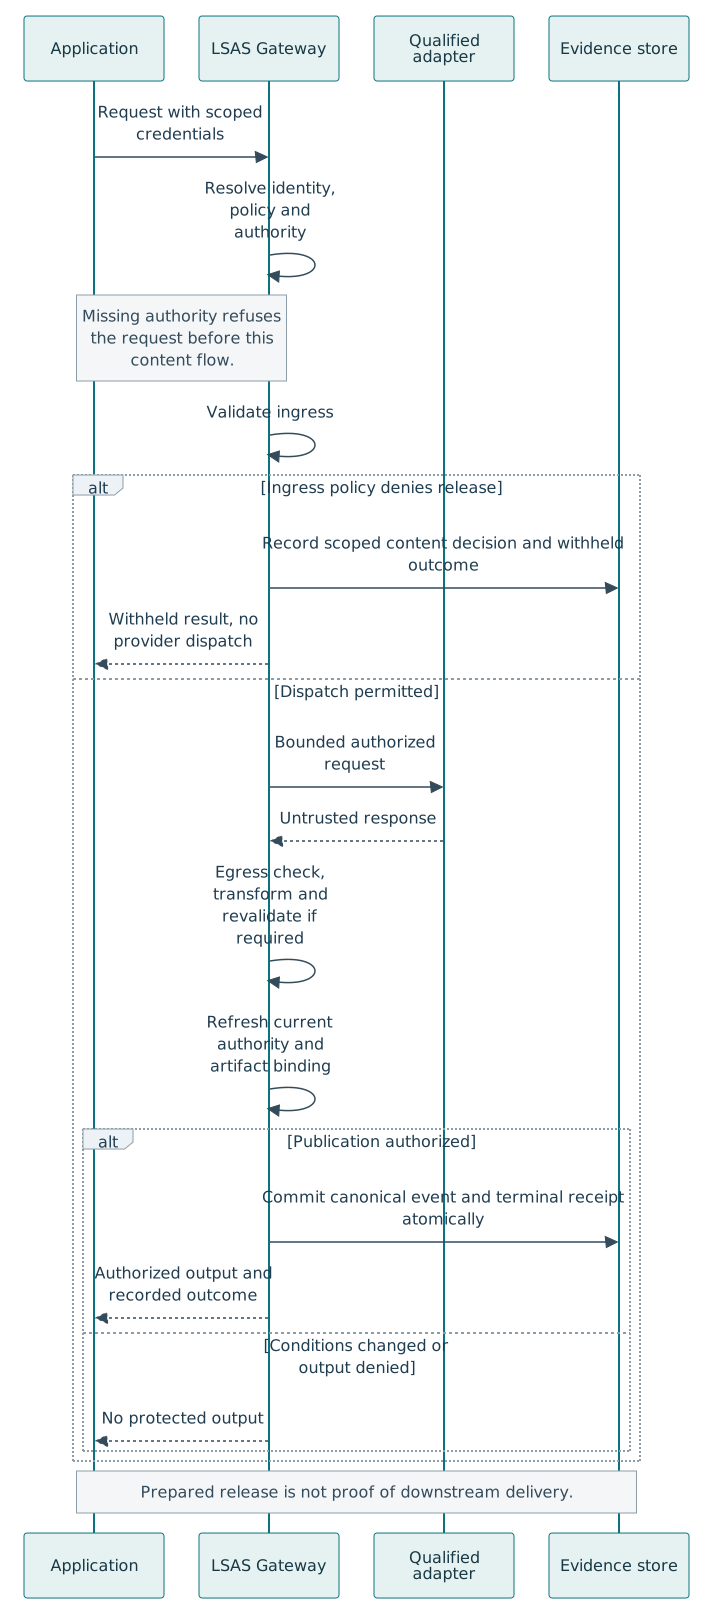
Ingress runs before permitted dispatch; output is checked and final authority is refreshed before atomic evidence publication and return.
Simplified sequence; ingress denial makes no provider call, while egress denial may follow execution.
Read the diagram description
Ingress runs before permitted dispatch; output is checked and final authority is refreshed before atomic evidence publication and return. Simplified sequence; ingress denial makes no provider call, while egress denial may follow execution.
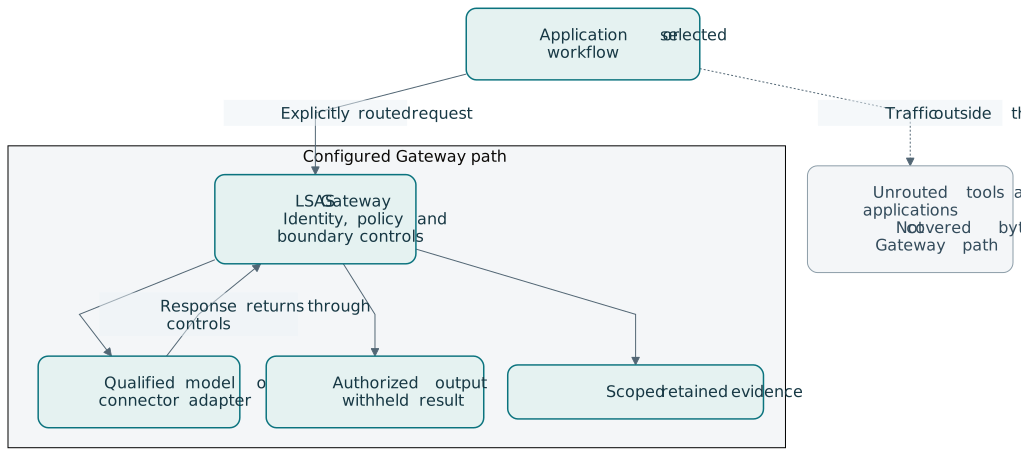
Only traffic routed through supported, configured Gateway paths receives those boundary controls. Other traffic is outside that enforcement path.
Supported inline/API placement; not organization-wide network interception.
Read the diagram description
Only traffic routed through supported, configured Gateway paths receives those boundary controls. Other traffic is outside that enforcement path. Supported inline/API placement; not organization-wide network interception.
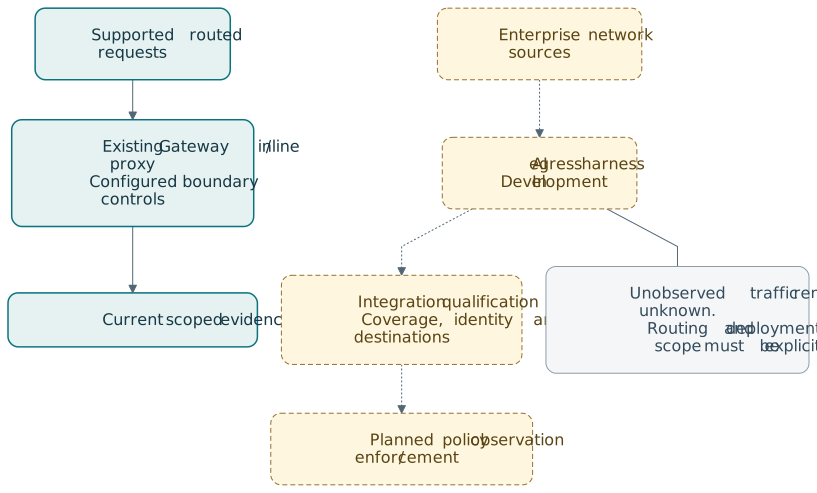
The current Gateway supports configured request paths. Broader enterprise egress integrations require explicit development and customer qualification.
Enterprise network harness is In Development; no universal traffic coverage claim.
Read the diagram description
The current Gateway supports configured request paths. Broader enterprise egress integrations require explicit development and customer qualification. Enterprise network harness is In Development; no universal traffic coverage claim.
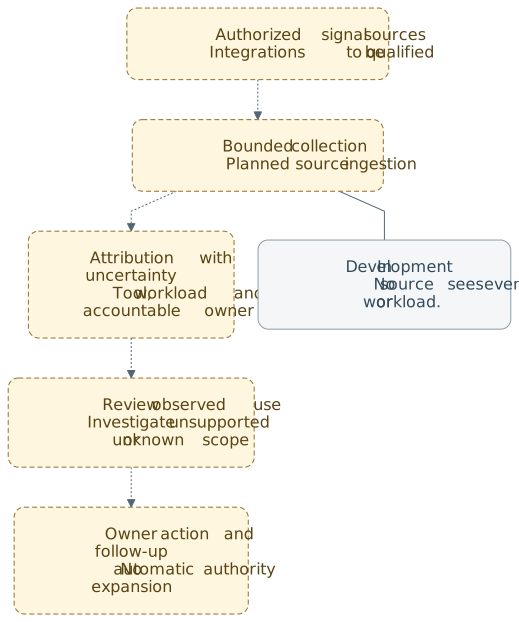
Planned discovery brings qualified signals into attribution and investigation; missing source coverage must remain visible.
In Development; this is a planned workflow, not a measured enterprise inventory.
Read the diagram description
Planned discovery brings qualified signals into attribution and investigation; missing source coverage must remain visible. In Development; this is a planned workflow, not a measured enterprise inventory.
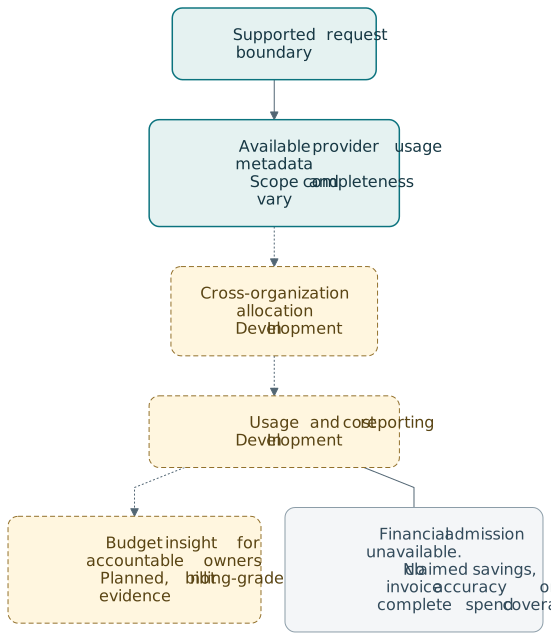
Provider usage metadata at a supported boundary is distinct from planned enterprise allocation, billing and financial controls.
Enterprise Tokenomics is In Development; financial admission is unavailable.
Read the diagram description
Provider usage metadata at a supported boundary is distinct from planned enterprise allocation, billing and financial controls. Enterprise Tokenomics is In Development; financial admission is unavailable.
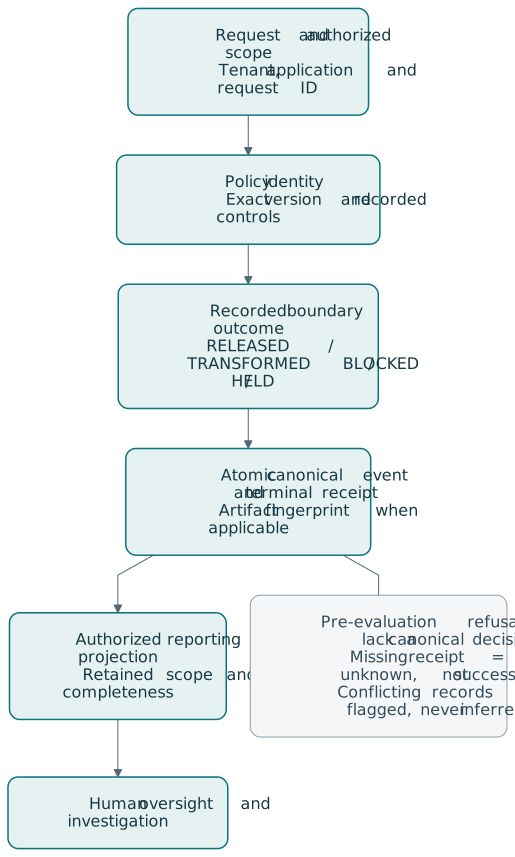
A request identity links the exact policy, recorded boundary outcome and artifact fingerprint to retained reports. Intermediate events do not establish release.
Evidence integrity within retained scope; transaction commit is not downstream delivery.
Read the diagram description
A request identity links the exact policy, recorded boundary outcome and artifact fingerprint to retained reports. Intermediate events do not establish release. Evidence integrity within retained scope; transaction commit is not downstream delivery.
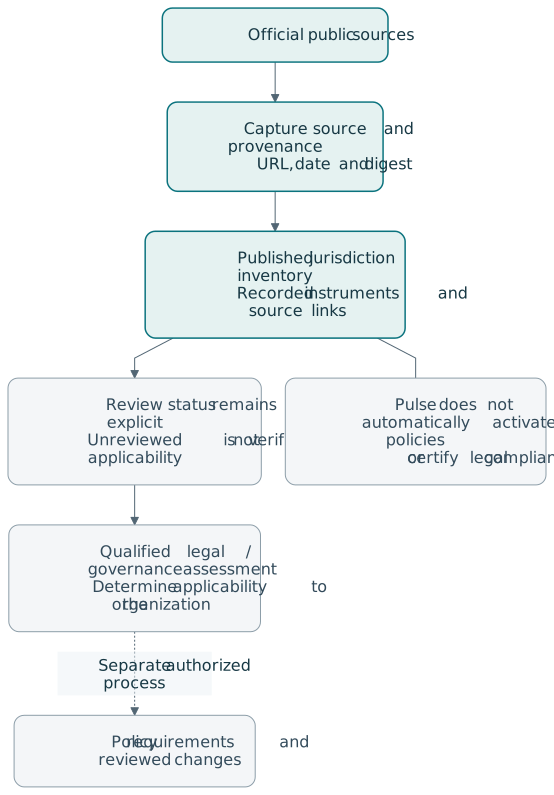
Official source records support a bounded published inventory. Review and applicability are separate from collection and publication.
Research inventory; a source record or enacted instrument is not an implementation obligation.
Read the diagram description
Official source records support a bounded published inventory. Review and applicability are separate from collection and publication. Research inventory; a source record or enacted instrument is not an implementation obligation.
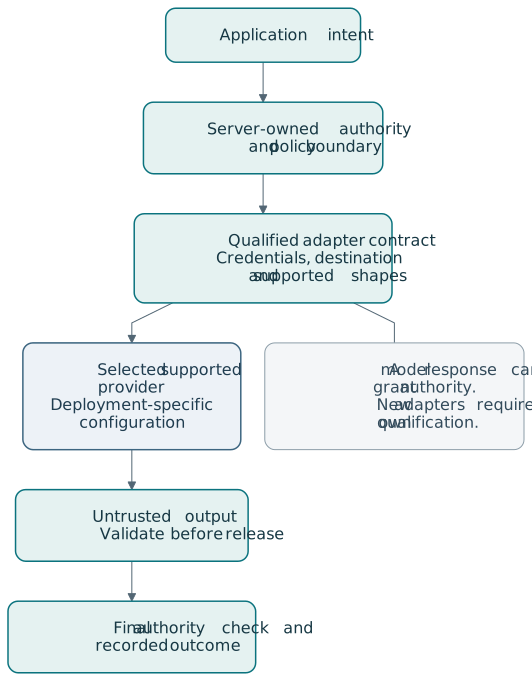
The governance boundary resolves authority and policy independently of model output, while each provider adapter has its own qualification requirements.
Adapter architecture is not universal provider or tool availability.
Read the diagram description
The governance boundary resolves authority and policy independently of model output, while each provider adapter has its own qualification requirements. Adapter architecture is not universal provider or tool availability.
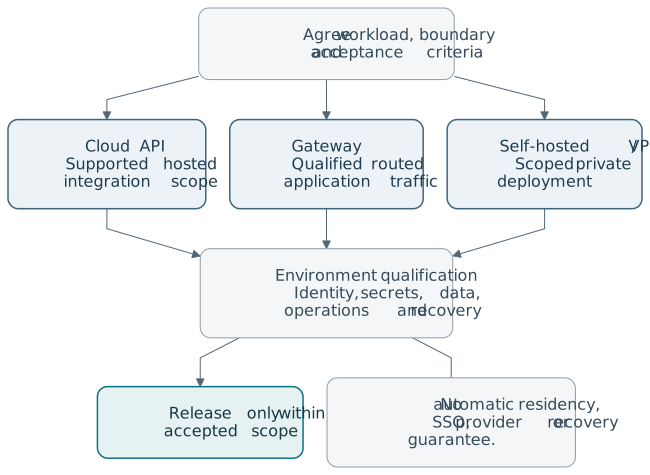
Cloud API, Gateway and private deployment options are scoped delivery patterns with common governance boundaries and distinct customer requirements.
Commercial architecture options; availability and readiness depend on the agreed deployment.
Read the diagram description
Cloud API, Gateway and private deployment options are scoped delivery patterns with common governance boundaries and distinct customer requirements. Commercial architecture options; availability and readiness depend on the agreed deployment.
Workload measurements, coverage and failure-mode evidence determine a justified operating envelope. Illustrations do not establish capacity.
Requires customer qualification; 100 / 3,000 / 30,000 profiles are illustrative, not benchmarks.
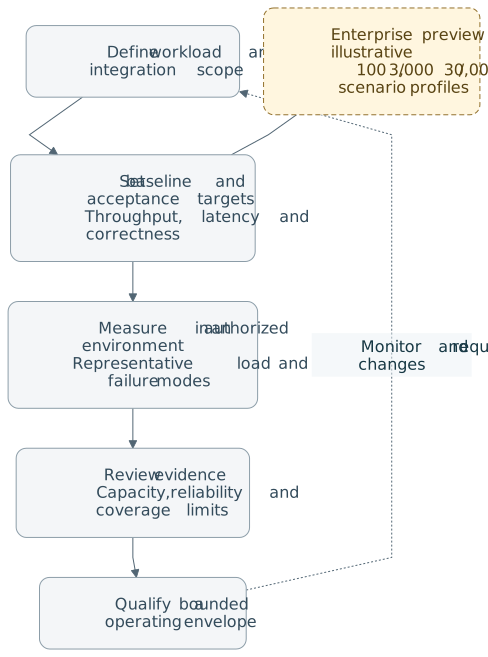
Read the diagram description
Workload measurements, coverage and failure-mode evidence determine a justified operating envelope. Illustrations do not establish capacity. Requires customer qualification; 100 / 3,000 / 30,000 profiles are illustrative, not benchmarks.
Reports share a retained, authorized relation while distinguishing totals, excerpts, unknown outcomes and event-time attribution.
Historical evidence uses recorded context, not current assignments; report scope and limits remain visible.
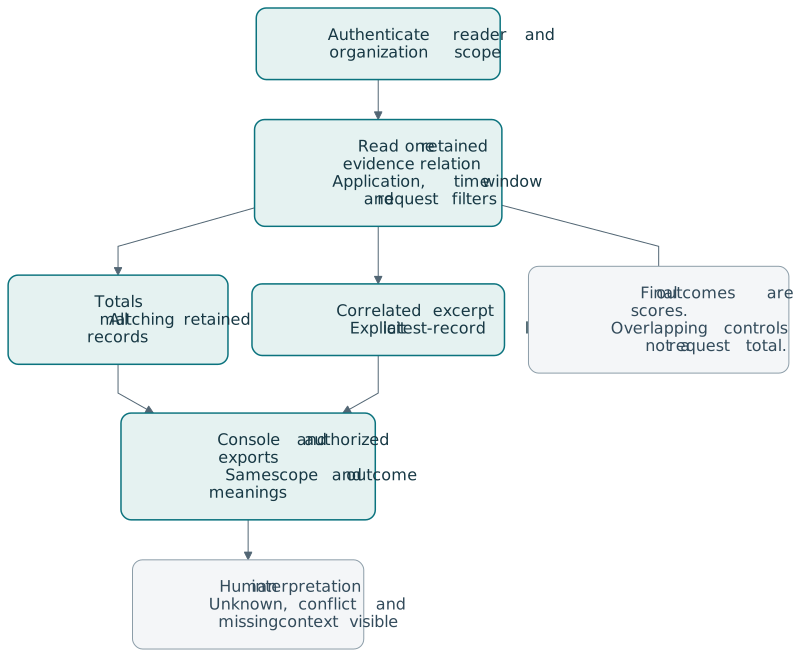
Read the diagram description
Reports share a retained, authorized relation while distinguishing totals, excerpts, unknown outcomes and event-time attribution. Historical evidence uses recorded context, not current assignments; report scope and limits remain visible.
Execution authority, content policy and final publication are separate gates; a hold never becomes permission through a UI override.
Current supported boundaries; public teaching simulations do not resume real effects.
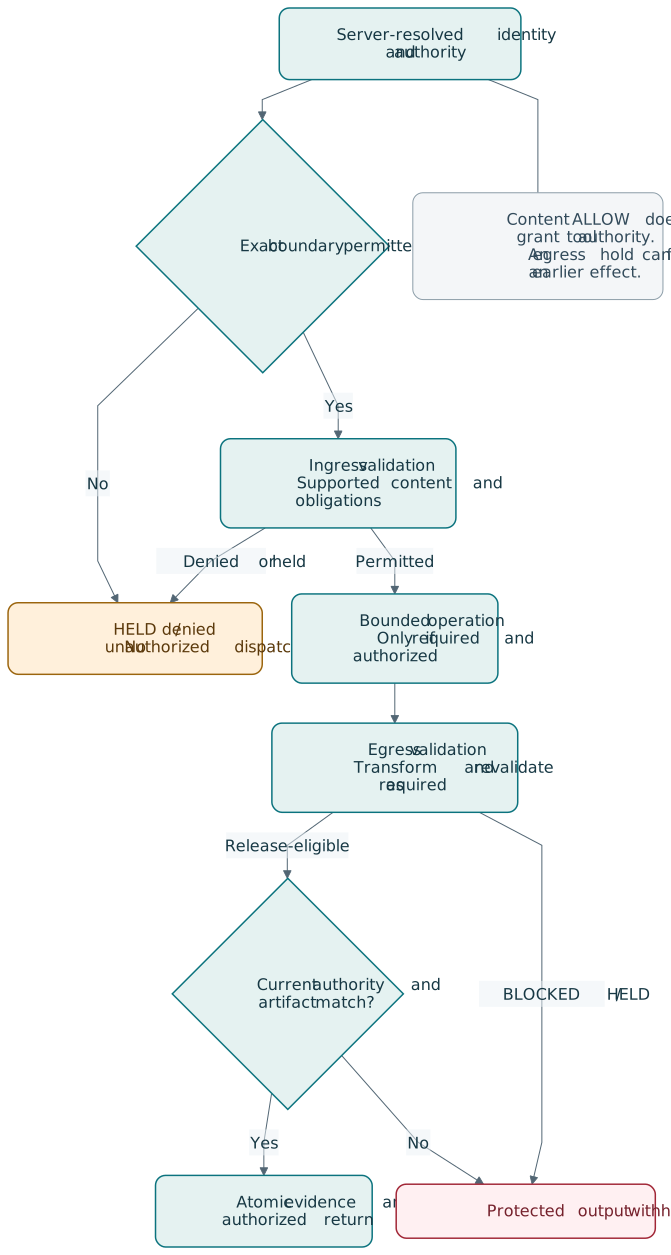
Read the diagram description
Execution authority, content policy and final publication are separate gates; a hold never becomes permission through a UI override. Current supported boundaries; public teaching simulations do not resume real effects.
Governance Workbench is a public demonstration context; Developer Evaluation is a separate private, bounded API experience.
Neither free path grants production entitlement or is a prerequisite for the other.
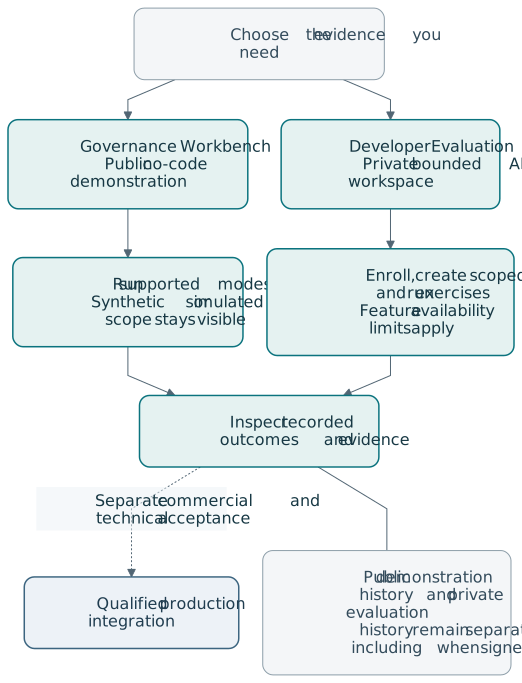
Read the diagram description
Governance Workbench is a public demonstration context; Developer Evaluation is a separate private, bounded API experience. Neither free path grants production entitlement or is a prerequisite for the other.
Untrusted clients and content cannot grant authority. Server authorization, qualified adapters and scoped evidence each have separate responsibilities.
Architecture boundaries; no certification or complete customer-environment qualification claim.
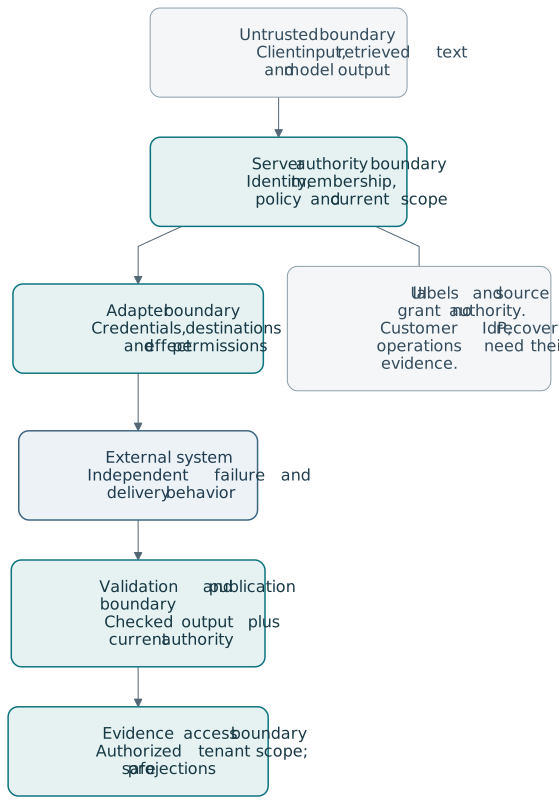
Read the diagram description
Untrusted clients and content cannot grant authority. Server authorization, qualified adapters and scoped evidence each have separate responsibilities. Architecture boundaries; no certification or complete customer-environment qualification claim.